


Background Verification Process
Purpose
This document sets out how Hybrowlabs verifies the background of every person engaged to work on customer accounts and how the depth of that verification is matched to the access the role will hold.
Our people work inside customer production instances, hosting consoles, source repositories and database backups. Verification exists so that a customer granting that level of access knows who has been placed on their account and on what basis.
Applicability
Every person engaged by Hybrowlabs is verified, including contractors, interns and subcontracted personnel. There is no category of delivery role that is exempt. What varies is the tier applied, not whether verification is performed.
Where personnel are supplied through a subcontracting organisation, that organisation is required to have performed equivalent verification and to evidence it before its people are given access. The organisation itself is assessed under the Vendor / Subprocessor Management Policy.
Verification tiers
Every role is assigned one of three tiers. The tier is set by the access the role will hold and by any requirement in the customer contract. Where more than one condition applies, the higher tier governs.
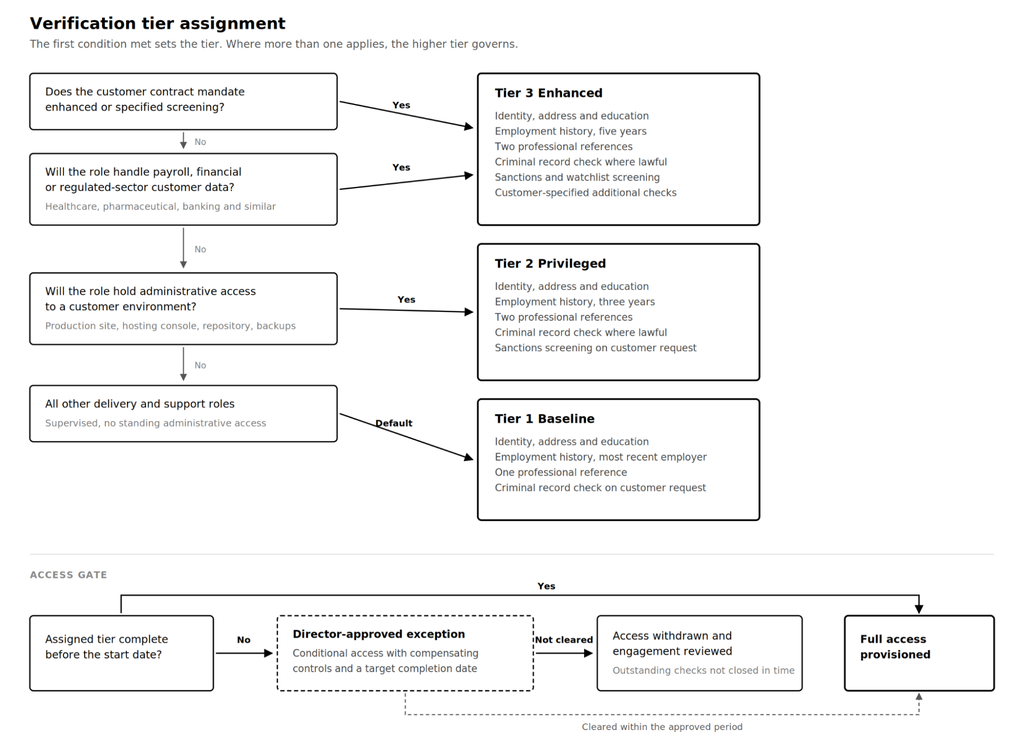
- Tier 1 applies to delivery and support roles working under supervision without standing administrative access.
- Tier 2 applies to roles holding administrative access to a customer production environment, hosting console, source repository or backup store.
- Tier 3 applies to roles handling payroll, financial or regulated-sector customer data and to any account where the customer contract mandates enhanced screening.
Where a customer specifies checks beyond those shown, they are added to the assigned tier for that account.
Consent and privacy
Verification is performed only with the written consent of the individual, obtained before any check begins. The individual is told which checks will be run and how the results will be handled.
Results are restricted to the director and the operations personnel who administer the process. They are not shared with project teams, are not disclosed to customers in raw form, and are held separately from general HR records.
Where verification is carried out by an external agency, that agency is assessed and recorded as a subprocessor, is bound by a written agreement, and is instructed to collect only the data required for the checks commissioned.
Timing
Verification is initiated once an offer or contract is accepted, and the intent is completion before the start date. Access to any customer environment is provisioned only after the applicable tier is complete, or under an approved exception.
Exceptions and conditional access
Where verification cannot be completed before the start date, typically because a previous employer or institution is slow to respond, the director may approve conditional access. The approval is written and records the reason, the checks outstanding, the compensating controls applied, and a target completion date.
Compensating controls for conditional access are the following:
- No standing administrative access to any customer production environment
- Work performed on non-production environments or under the supervision of a verified team member
- No access to payroll, financial or regulated-sector customer data
- Access scoped to a single account rather than the general delivery estate
If the outstanding checks are not cleared by the target date, access is withdrawn and the engagement is reviewed. If a check returns an adverse finding, access is suspended pending the director's review, and the outcome may be withdrawal of the offer or termination of the engagement.
Re-verification
Verification is repeated where an individual moves into a role that carries a higher tier, where a customer contract requires periodic re-screening, and where a gap in engagement of more than twelve months has occurred.
Retention
Verification records are retained for the duration of the engagement and for the period required by applicable law and customer contract, then deleted. Deletion is recorded.
Evidence maintained
Hybrowlabs can produce the following for customer due diligence or audit, subject to redaction of personal data:
- Signed consent record
- Tier assigned and the basis for it
- Verification status and completion date per individual
- Conditional access approvals, compensating controls and closure records
- Adverse finding reviews and outcomes
- Agency agreement where an external provider is used
- Retention and deletion records
Customers are provided with confirmation of verification status against named personnel. Underlying personal data is not disclosed.
Related documents
- HR Security Policy
- Acceptable Use Policy
- NDA / Confidentiality Agreement Structure
- Vendor / Subprocessor Management Policy
- Subprocessor Register